How Was the Supermarket Refrigeration System Sabotaged Remotely?
France, October 2026 – A Technical Analysis of the Cyberattack on Refrigeration Controllers 20 Oct 2026 · Ege ENÇ What Happened in Brief On the night of October 11–12, 2026, attackers remotely switched the refrigerators and freezers of hundreds of supermarkets in France into defrost mode. Cabinet temperatures rose for hours, the cold chain was […]
 egenc
France, October 2026 – A Technical Analysis of the Cyberattack on Refrigeration Controllers
20 Oct 2026 · Ege ENÇ

What Happened in Brief
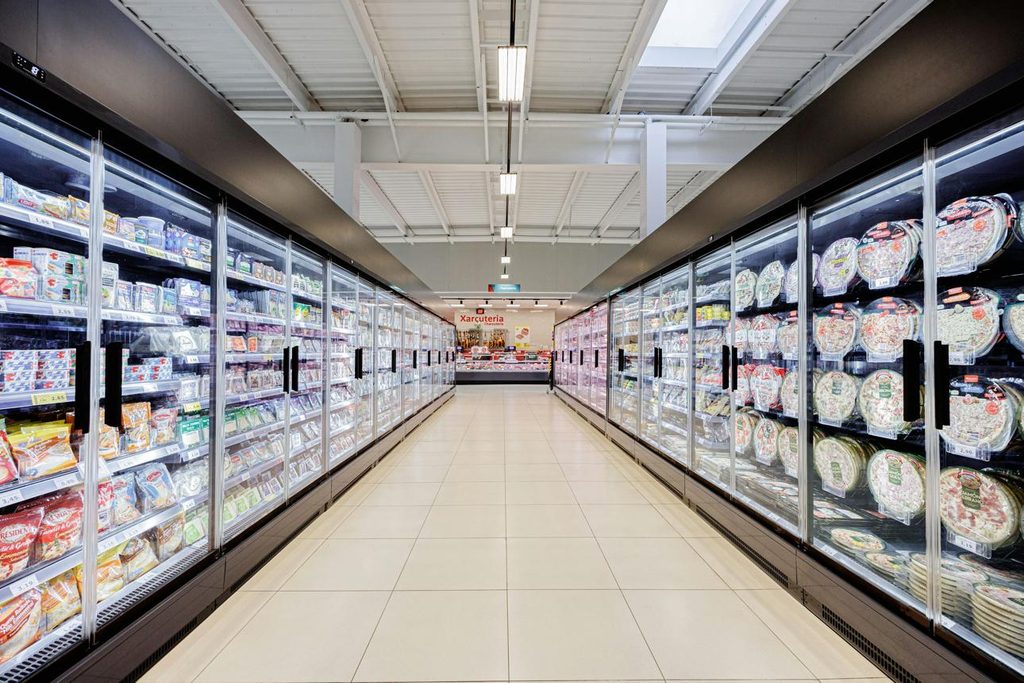
On the night of October 11–12, 2026, attackers remotely switched the refrigerators and freezers of hundreds of supermarkets in France into defrost mode. Cabinet temperatures rose for hours, the cold chain was broken, and fresh and frozen products were destroyed on a massive scale.
The number of affected stores varies by source: Reuters reported at least 350, the BBC estimated approximately 400 based on retail-chain data, and French Finance Minister Roland Lescure told parliament that approximately 700 of the country’s roughly 10,000 supermarkets were affected. The chains included Intermarché, Netto, Coopérative U (Super U), Carrefour Market, Monoprix, and E.Leclerc. Damage estimates range from several million euros for a single retail group to “tens of millions of euros per day” nationwide; losses of €270,000 were reported at just two supermarkets in Alsace.
The attack was described as the first major incident to physically affect a country’s food supply chain, demonstrating how a weakness in an internet-connected OT (operational technology) controller can translate into physical damage. As of October 20, 2026, how the attack was carried out is largely understood; however, the vulnerability or port used for initial access has not been officially confirmed.
How the Refrigeration System Works and What Was Targeted
In a large supermarket, each cabinet does not operate independently. A central system manager monitors the temperatures of all refrigeration circuits, manages alarms, and schedules operating hours and defrost cycles. This central controller connects to the local controllers of each cabinet and compressor group through an internal field bus (Modbus/LON). The only component that needs a connection to the outside world is the web management interface used for remote maintenance; the field bus should remain internal.
Refrigeration contractors often expose this interface to the internet so that they can perform maintenance without sending technicians to the site. Stores generally acquire the equipment through refrigeration contractors rather than directly from Danfoss, which leaves responsibility for patching and network security fragmented.
In the French incident, CERT-FR reported compromises involving four product families: the Danfoss AK-SM and AK-SC series, and Copeland XWEB and Dixell XWEB systems. According to Danfoss, most affected devices were AK-SM 800 (discontinued in 2021) and AK-SC 355 (2016) models that no longer receive security updates; affected units of the newer AK-SM 800A were running outdated firmware. Danfoss’s remote management interface is known as StoreView.
The Mechanics of the Attack: A Harmless Maintenance Function Becomes a Weapon
Defrosting is a normal maintenance function in refrigeration: a heating element briefly activates to melt ice that has accumulated on the evaporator. Freezers generally run a short defrost cycle at night, during which the temperature rises slightly. The problem was that the attackers could interfere with the settings of this function.
According to Le Monde, the defrost target temperature was raised to 50 °C in some systems, and a cycle that normally lasted about one hour was extended to eight hours. Together, these two changes had two effects:
- They effectively stopped cooling for hours; the cabinets warmed throughout the night. Intermarché reported that cabinets in approximately 150 of its stores reached up to 50 °C for six hours; some cabinets at a supermarket in Normandy reportedly reached 80 °C.
- They delayed warnings. Because the extended cycle appeared to be a “normal” defrost operation, the alarms were also triggered late; moreover, in many locations no night-shift staff were available to intervene.
The impact was not limited to a malfunction displayed on a screen. In some stores, overheating caused smoke, small fires, and water damage when fire-suppression systems activated; the Paris prosecutor’s office confirmed that fires had begun. Because the cold chain could no longer be reliably maintained, otherwise saleable food had to be discarded—one Intermarché store alone destroyed several tonnes of products.
Technical Root Cause: An Exposed Interface + the “Code of the Day”
Two weaknesses came together. The first was that the management interface had been left directly accessible from the internet—contrary to good practice and the first issue highlighted by CERT-FR. The second was a structural weakness in these devices’ authentication.
The Danfoss AK-SM series includes a “code of the day” mechanism: a service-access feature designed so that a manufacturer’s technician can log in without knowing the customer’s password. The problem is that the device’s date is the only input to this code, and the algorithm can be reverse-engineered from the software. In other words, the password is a value derived, roughly speaking, from “today’s date,” without cryptography (no hash or HMAC), and can be calculated offline without touching the device. The username was admin, while the password was the code generated from that day’s date—and it was the same across the fleet.
Research published by Claroty Team82 on August 9, 2026 (“Freeze the Controller, Defrost the Food”) identified three vulnerabilities in the AK-SM 800A’s embedded web interface:
| CVE | Type | CVSS v3 | Notes |
|---|---|---|---|
| CVE-2025-41450 | Authentication bypass (code of the day) | 8.2 | Date-based password generation; full administrator session |
| CVE-2025-41451 | Command injection (SMTP email setting) | 7.6 | Post-authentication remote code execution (RCE) |
| CVE-2025-41452 | Nginx configuration injection | 5.4 | Post-authentication DoS |
These were fixed in firmware R4.3.1. For older end-of-life (EOL) devices, Synacktiv had published a similar “code of the day” bypass for the SM800 and SC255/SC355 in 2023 (check_code_of_day, triggered by the eds_only/quantum_only attribute instead of a password); for those models, Danfoss recommended restricting network access as the only mitigation. The AK-SM 800A also had CVE-2023-25913/25914/25915 from 2023 (the last of these allowed post-authentication RCE, CVSS 9.8/9.9), which were fixed in version 3.3.
According to laboratory analyses by the Ironhackers team, bypassing this security barrier relies on a fairly simple procedure. All that is needed is to send the “password of the day” to the system’s POST /xml.cgi endpoint with the parameters action=”getauth” and eds_only=”1″. The system responds to these attempts like an oracle, clearly indicating through its HTTP response whether the submitted password is correct or incorrect. Once the correct password is found through brute force, the system grants the attacker a fully privileged administrator session (authtype=0xFFFFFF). The most dangerous part is that this administrator access extends directly to the management of the refrigeration systems (Case Control). In other words, someone who gains access can manipulate the cabinets’ temperature settings and modify the defrost processes at will.
Which Software, Which Port, Which Vulnerability: What Is Known and Unknown
A clear distinction is needed here, because news reports often treat the “code of the day” bypass and the French attack as though they were one and the same confirmed fact.
Ports. The AK-SM 800 installation manual shows that its web interface uses TCP port 80 by default and lists port 3001 for XML communication. The AK-SM 800A manual lists TCP ports 80 and 443 for web access. These are ports the devices can use. No publicly available network record has confirmed which port the attackers used in this incident; the manual alone does not justify saying, “It definitely happened over port 80.”
Initial access method. As of October 20, 2026, the vulnerability used for initial access had not been officially established. The CERT-FR bulletin does not identify a specific CVE or firmware version; a source close to Lecornu’s office said only that ANSSI had found a flaw in Danfoss software, but that flaw had not been disclosed. Claroty’s findings are real and have been patched, but there is no confirmation that these flaws were exploited in France, and older EOL device models were also involved. Therefore, a single date-derived password cannot be held responsible for the entire incident.
What Is Known and What Remains Possible.
| Topic | Status |
|---|---|
| Physical effects (defrost, 50 °C, 8 hours) | Confirmed (retail-chain statements, Le Monde, CERT-FR) |
| Targeted product families (AK-SM, AK-SC, Copeland/Dixell XWEB) | Confirmed (CERT-FR) |
| Most devices were EOL or running old firmware | Confirmed (Danfoss) |
| Internet-exposed interfaces were a prerequisite | Confirmed (scanning data) |
| Initial access used the “code of the day” bypass | Possible but unconfirmed |
| Which port was used | Unknown |
| Identity / motivation of the attackers | Unknown |
Experts generally agree that the attack was not technically “sophisticated”: well-known weaknesses combined with exposed interfaces amounted to, in the words of Ken Munro of Pen Test Partners, “pushing on an open door.” This leaves open whether the perpetrator was a state-backed actor or “kids playing games.”
The Scale of Exposure: Why Were So Many Devices Accessible?
A prerequisite for this attack was that large numbers of controllers were directly exposed to the internet. Measurements taken by scanning companies in the days before the attack show that this exposure had existed for months.
Different scanners reported different numbers because their methodologies differed; these figures should not be added together as if they represented a single trend. In August, Claroty counted 2,765 exposed AK-SM 800A units with Censys. Around the time of the attack, Reuters found at least 4,500 Danfoss interfaces on Shodan, while Baptiste Robert of Predicta Lab found 2,752 devices (1,590 of them in France). In IPinfo’s consistent, single-source count, France had 1,331 panels—more than the rest of the world combined—and 85% of them were running software with known vulnerabilities; most had been exposed at the same address for at least six months.
It is not clear why France stood out so strongly, but the data rule out some explanations: French panels were not less well patched than those in other countries (the proportion running vulnerable software was around 84% elsewhere, too). The difference was that far more of these systems were online in France. Poland ranked second after France with 179 panels; following the attack, most French operators removed their devices from the internet (only 316 were still exposed on October 14).
Investigation, Attribution, and Open Questions
The Paris prosecutor’s office opened an investigation on its own initiative through its cybercrime division and referred the case to the national cybercrime office, OFAC. Prime Minister Sébastien Lecornu asked ANSSI to investigate the incident and coordinate with other European countries.
What makes the investigation unusual is that no group claimed responsibility for the attack and no ransom demand was made. A source close to the investigation said this puzzled investigators: hacktivists typically claim credit immediately, while cybercriminals make financial demands. This absence leaves the perpetrator’s identity open—from a state actor to “kids playing games.” As Munro put it, if a state were behind it, why would it target only some French refrigeration cabinets?
The geographical scope of the incident is also unclear. An analyst from Sekoia said Spain, Portugal, Poland, Germany, and Belgium had also been affected; all of these countries had outdated, exposed Danfoss panels before the attack, but whether they were actually affected has not been confirmed.
The most striking parallel is in the United States: Reuters noted similarities between the French attack and refrigeration outages at roughly a dozen U.S. military commissaries in late August. Fort Huachuca in Arizona reported that all of its commissary freezers had entered defrost mode; three military criminal investigation units were examining the incidents. There is no confirmed link between the two events, but the resemblance is notable.
At the same time, Dutch company Ahold Delhaize experienced a cybersecurity incident; both the Netherlands and the company said they saw no connection to the French incident.
Technical Lessons and Defenses
The central lesson of the incident is architectural: if a management interface left accessible for remote maintenance is compromised, an attacker can do more than view data; they can change the physical work performed by the device. Compromising an IT network means losing data; compromising an OT controller means losing the cold chain—in other words, the physical process itself. A routine maintenance function such as “defrost” can become a weapon as soon as its settings can be controlled.
CERT-FR’s recommendations address this point directly:
MOST IMPORTANT: Remove direct internet access to the control devices (and, more generally, to all units with public IP addresses).
Secure access: Allow remote access only through a secure VPN or protected network; filtering contractor IP addresses at the firewall is an emergency patch, not a permanent solution.
Software intervention: Review the entire configuration, particularly the defrost schedules—this is what the attackers modified.
Up-to-date software: Update firmware on supported devices, set the security level to Strict mode, and change default passwords.
General OT/ICS (operational technology/industrial control systems) takeaway: These devices are often old, highly customized, and designed without security in mind. Every internet-exposed “building system” (refrigeration, ventilation, energy management) should now be considered part of an incident response plan.
References
Official / Manufacturer
- CERT-FR (ANSSI) alert CERTFR-2026-ALE-012, affected product families and recommendations
- Danfoss security advisory DSA-2023-08-01, CVE-2023-25913/25914/25915
- CISA ICS advisory ICSA-25-140-03, AK-SM 8xxA authentication bypass
- Danfoss StoreView overview
- AK-SM 800 installation manual (PDF), TCP 80, XML 3001
- AK-SM 800A user manual (PDF), TCP 80/443
Technical Research
- Claroty Team82, Freeze the Controller, Defrost the Food, CVE-2025-41450/41451/41452
- Synacktiv, SM800 & SC255/SC355 auth bypass (2023, PDF)
- Ironhackers, CVE-2025-41450 technical analysis (laboratory)
- IPinfo, France’s Supermarket Fridges Were Vulnerable Online for Months, exposure data by country
News / Incident
- Reuters, Investigators hunt French supermarket fridge hackers
- Le Monde, A disastrous day for French supermarkets
- Cooling Post, Danfoss moves to mitigate cyberattack
- ComplexDiscovery, Refrigeration hack affected about 700 French supermarkets
- Wikipedia, 2026 French supermarket refrigerator hack
- BBC Turkish-language report
Data are current as of October 20, 2026. Scanning counts are lower bounds and are based on different methodologies; they should not be combined as a single trend.
About the author
egenc
Subscribe to the newsletter
New cybersecurity articles, research and hardware-lab notes — straight to your inbox.
Related articles
CVE-2026-37603 & CVE-2026-37604: Admin Brute-Force Protection Bypass Chain in pH7Builder
CVE-2026-25769 Analysis: Remote Code Execution in Wazuh Cluster via Insecure Deserialization