CyberMap Blog
Writing and analysis on offensive security, compliance and defense.
How Was the Supermarket Refrigeration System Sabotaged Remotely?
France, October 2026 – A Technical Analysis of the Cyberattack on Refrigeration Controllers 20 Oct 2026 · Ege ENÇ What Happened in Brief On the night of October 11–12, 2026, attackers remotely switched the refrigerators and freezers of hundreds of supermarkets in France into defrost mode. Cabinet temperatures rose for hours, the cold chain was […]
Read More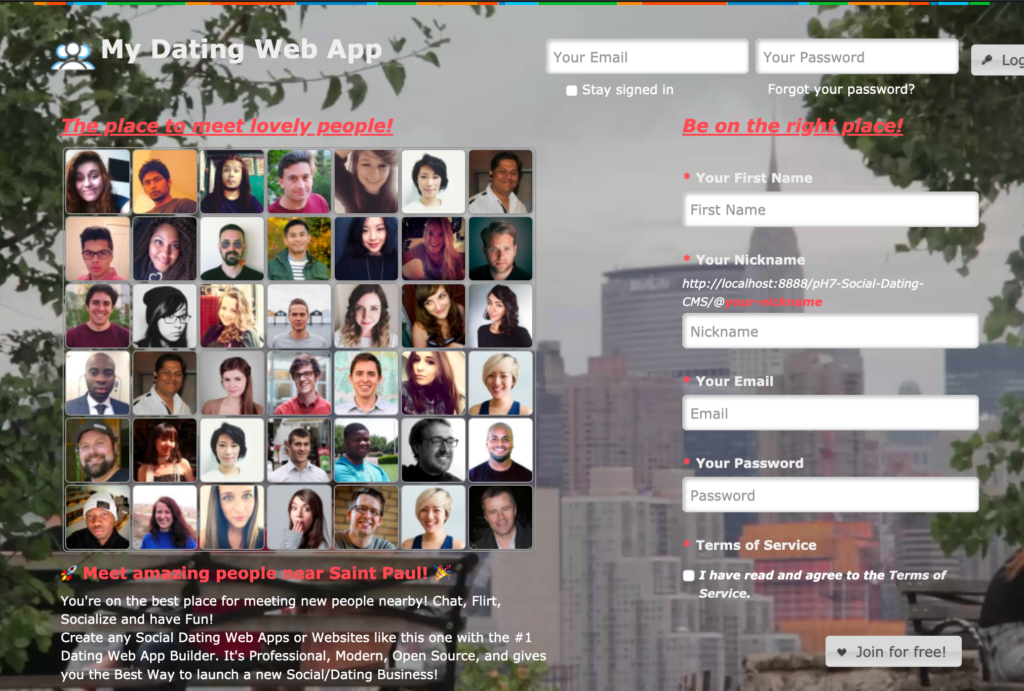
CVE-2026-37603 & CVE-2026-37604: Admin Brute-Force Protection Bypass Chain in pH7Builder
CVE: CVE-2026-37603 (CWE-307) · CVE-2026-37604 (CWE-290)CVSS v3.1: 6.5 (Medium) for each vulnerabilityAffected versions: ≤ 18.2.0 (both) · ≤ 19.2.0 (CVE-2026-37603 only)Fixed in: 18.3.0 for CVE-2026-37604. CVE-2026-37603 unfixed at time of writing An attacker who can reach the administration panel of an affected pH7Builder installation over the network can guess administrator passwords without any of the […]
CVE-2026-25769 Analysis: Remote Code Execution in Wazuh Cluster via Insecure Deserialization
1. Introduction – Executive Summary Security monitoring platforms are among the most privileged systems on a corporate network: they collect logs from every endpoint, monitor file integrity, and — when needed — push commands back down to those endpoints. Compromising such a platform therefore carries consequences far beyond the loss of a single server. CVE-2026-25769 […]
CVE-2026-31431 Technical Analysis: The “Copy Fail” Local Privilege Escalation Vulnerability in the Linux Kernel
1. Introduction – Executive Summary In the cybersecurity world, local privilege escalation (LPE) vulnerabilities are usually carried out through file permissions, misconfigured services, or complex memory overflows. CVE-2026-31431 — disclosed publicly in late April 2026 and codenamed “Copy Fail” — breaks that pattern entirely. It abuses the Linux kernel’s zero-copy mechanisms and cryptographic pipelines to […]
WordPress REST API Batch Endpoint Exploit Chain (wp2shell): From Route Confusion to Remote Code Execution
CVE: CVE-2026-63030, CVE-2026-60137CWE: CWE-436, CWE-89CVSS: 9.8 (Critical)Affected versions: WordPress 6.9.0–6.9.4, 7.0.0–7.0.1Fixed in: 6.9.5 / 7.0.2 / 6.8.6Vulnerability Chain codename: wp2shell A content management system that powers a large share of the public web was, in its default installation, fully compromisable by an attacker holding no account and requiring no plugins to be present. The only […]
Grand Larceny Auto — Client-Side Trust Bypass to Hardcoded Secret Disclosure
Room: Grand Larceny Auto A locally-installed, single-player crime-simulator game hides a bonus reward behind an in-game vault that the game itself states can only be opened by reaching a police “wanted” reputation level one step higher than the maximum the game ever lets a player reach through normal play. Anyone willing to open the game’s […]
Fools Mate: Revenge — Prototype Pollution to Global Authorization Bypass
Room: Fool’s Mate: Revenge A browser-based puzzle app let any visitor claim a reward that was meant to be granted only to accounts the operator had specifically approved, without ever creating an account, logging in, or guessing a credential. One crafted request was enough to flip that approval flag — and because of where the […]
Technically Identical, Legally Opposite: The Fine Line Between Penetration Testing and Cybercrime
A question frequently arises in conversations with enterprise clients: “If the actions performed by penetration testing professionals technically resemble a cyberattack, how is this service considered legal?” This question points to one of the fundamental paradoxes of the cybersecurity industry. Indeed, the tools, methods, and techniques used by a penetration tester and a cybercriminal are […]
Subscribe to the newsletter
New cybersecurity articles, research and hardware-lab notes — straight to your inbox.